CVE-2025–61882 Explained: Why Cyber Security Testing Can’t Be Ignored

In today’s fast-moving digital landscape, vulnerabilities don’t just expose systems; they expose assumptions. CVE-2025–61882 is a strong reminder that even mature applications can become attack surfaces when security is not continuously tested and monitored.
As cyber threats evolve, organizations offering digital products and services must move beyond reactive fixes and adopt a proactive cyber security mindset.

Understanding CVE-2025–61882 in Simple Terms
CVE-2025–61882 highlights how weaknesses in application logic or input handling can be exploited by attackers to gain unauthorized access, disrupt services, or manipulate system behavior.
What makes vulnerabilities like this dangerous is not just the flaw itself, but how silently it can be abused if left undetected.
This is where strong cyber security services play a critical role.
Why Vulnerabilities Like This Matter to Businesses
Many organizations believe attackers only target large enterprises. In reality, attackers go after:
- Applications with poor validation
- Systems without regular security testing
- Businesses that assume “basic security is enough.”
A single vulnerability can lead to:
- Data breaches
- Service downtime
- Compliance violations
- Loss of customer trust
Cyber security is no longer optional — it’s foundational.
How Attackers Typically Exploit Such Weaknesses
While we avoid sharing exploit-level details, attackers usually follow patterns like:
- Identifying unvalidated inputs
- Manipulating requests or parameters
- Bypassing expected workflows
- Escalating access silently
Without continuous monitoring, such activity can remain invisible for weeks or even months.
How to Reduce Risk from Similar CVEs
Organizations can significantly reduce exposure by adopting the following practices:
1. Continuous Vulnerability Assessment
One-time testing is not enough. Applications change, and so do threats.
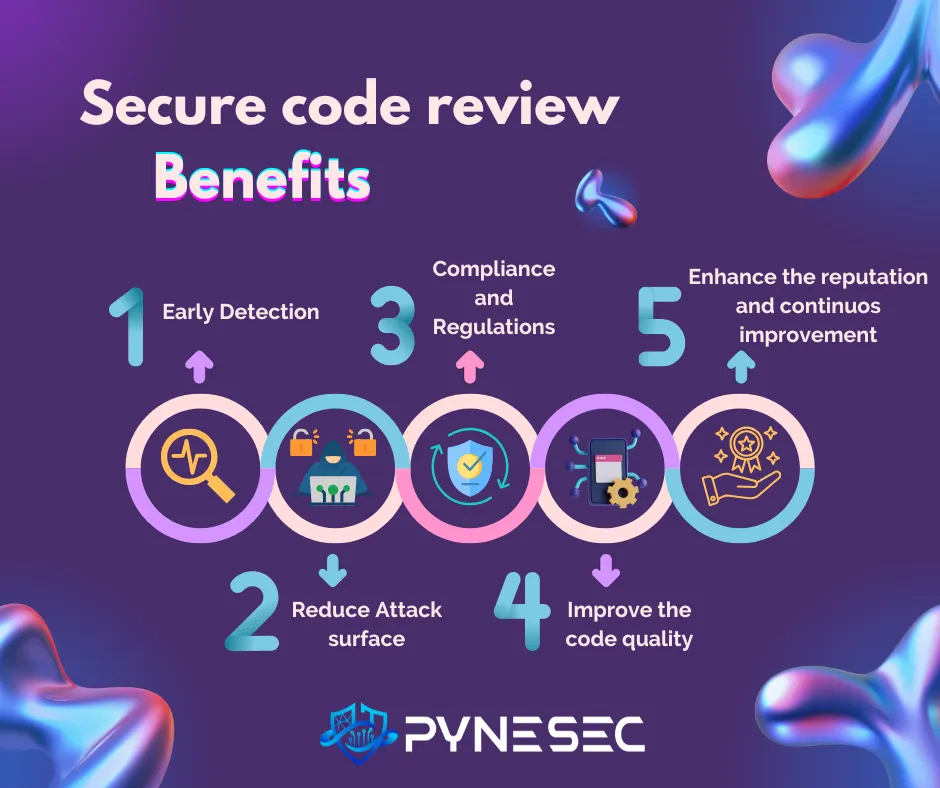
2. Secure Code Review
Many vulnerabilities originate at the code level. Reviewing logic and validation mechanisms early saves cost and risk later.
3. Web & API Security Testing
Modern applications rely heavily on APIs, making them prime targets for exploitation.
4. Security Monitoring & Incident Response
Detection matters as much as prevention.
How Pynesec Helps Organizations Stay Secure
At Pynesec, we focus on practical, real-world cyber security services that help organizations identify and mitigate risks before attackers do.
Get Pynesec’s stories in your inbox
Join Medium for free to get updates from this writer.
Our approach includes:
- Web application and API security testing
- Vulnerability assessment and penetration testing (VAPT)
- Secure architecture and remediation guidance
- Continuous security improvement strategies
We believe cyber security should enable growth, not slow it down.
Final Thoughts
CVE-2025–61882 is not just another vulnerability — it’s a reminder that security must evolve with technology. Organizations that invest early in cyber security services are far better prepared to face emerging threats.
If your application hasn’t been tested recently, now is the time.
About the Author
Pynesec is a cyber security services company helping businesses strengthen their applications, infrastructure, and digital trust through proactive security solutions.
👉 Want to strengthen your business security? Get in touch with us today.
#CyberSecurity #CyberSecurityServices #WebSecurity
#ApplicationSecurity #VulnerabilityManagement #PenetrationTesting #EthicalHacking #APIsecurity #InfoSec #Pynesec