Cyberdefenders — Insider Labs

URL Link: https://cyberdefenders.org/blueteam-ctf-challenges/insider/
Category: Endpoint Forensics
Tactics: Execution | Credential | Access | CollectionImpact
#################
Scenario:
After Karen started working for ‘TAAUSAI,’ she began to do some illegal activities inside the company. ‘TAAUSAI’ hired you as a soc analyst to kick off an investigation on this case.
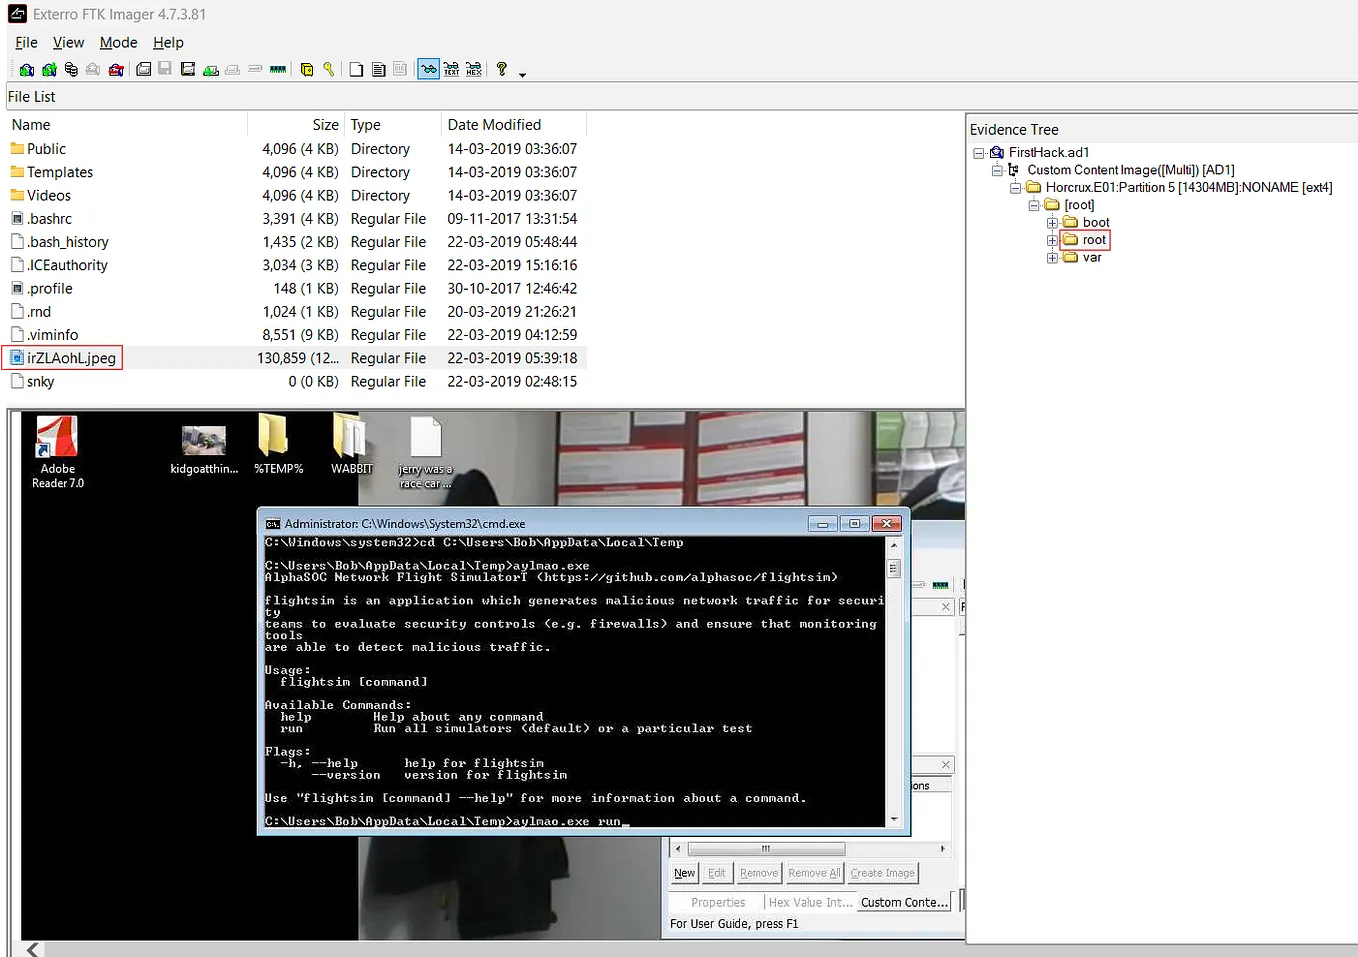
You acquired a disk image and found that Karen uses Linux OS on her machine. Analyze the disk image of Karen’s computer and answer the provided questions.
Tools:
Get Yufan Limbu’s stories in your inbox
Join Medium for free to get updates from this writer.
Reference Link for Tools:
- What distribution of Linux is being used on this machine?

2. What is the MD5 hash of the apache access.log?

3. it is believed that a credential dumping tool was downloaded? What is the file name of the download?

4. There was a super-secret file created. What is the absolute path?

5. What program used didyouthinkwedmakeiteasy.jpg during execution?

6. What is the third goal from the checklist Karen created?

7. How many times was apache run?

8. It is believed this machine was used to attack another. What file proves this?

9. Within the Documents file path, it is believed that Karen was taunting a fellow computer expert through a bash script. Who was Karen taunting?

10. A user su’d to root at 11:26 multiple times. Who was it?

11. Based on the bash history, what is the current working directory?

############ Happy Ending ############

I successfully completed the challenges. It was a great learning experience investigating Linux machines. This was a easy challenge, and it took me 2 hours to solve the box. CyberDefender has tons of challenges focused on blue team operations, making it a fantastic learning platform for blue teamers.