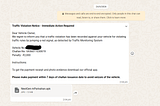
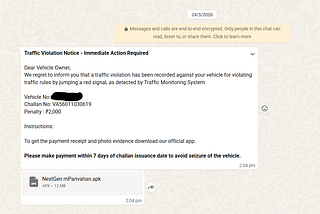
Jay Pomal·Sep 12Anatomy of a Fake Government App: Dissecting an Android Dropper Disguised as “mParivahan”A file lands in your inbox or, more realistically, arrives as a WhatsApp forward, an SMS about an “unpaid traffic challan,” or a link…
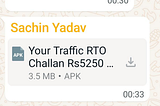
Kurious Kakashi·Mar 16RTO-challan APK Malware Analysis : Static analysis Writeup #1So I got this APK from my friend, and at that time I was starting my android malware analysis journey, so I thought why not analyze it…
Saravana·Oct 21, 2025SPYWARE MALWARE ANALYSISMalicious code or behavior that secretly collects user data or sends it elsewhere without clear permission is considered spyware.A response icon1A response icon1
luiz boina·Nov 5, 2024Android Malware Analysis II: Russian RAT & Its Anti-Analysis TechniquesIn this article, I present an analysis of an Android malware sample obtained last month. The malware uses anti-analysis techniques to…
Jimmy Shah·May 25, 2024Protecting the ‘Metaverse ecosystem’…: Openness is healthyMeta’s Reality Labs has an opening for “Malware Reverse Engineer”. Not an uncommon role, but this particular one is a bit more specific…
Dixon·Jan 6, 2024Analysis Practice on Chameleon Android Malware SampleThis is my analysis practice for an Android Malware known as the Chameleon Banking Trojan.
InOpenCTI.BRbyIalle Teixeira·Jun 10, 2023[UPDATE] FantasyMW(v2) Android Banking Trojan ressurge com novos alvosEm uma publicação anterior datalhamos o funcionamento e comportamento do FantasyMW, recentemente o Threat Actor realizou algumas alterações…