write up (IDOR)

IDOR (Insecure Direct Object Reference) is one of the most common yet dangerous
web application vulnerabilities. It occurs when an application exposes internal object references without proper authorization checks.
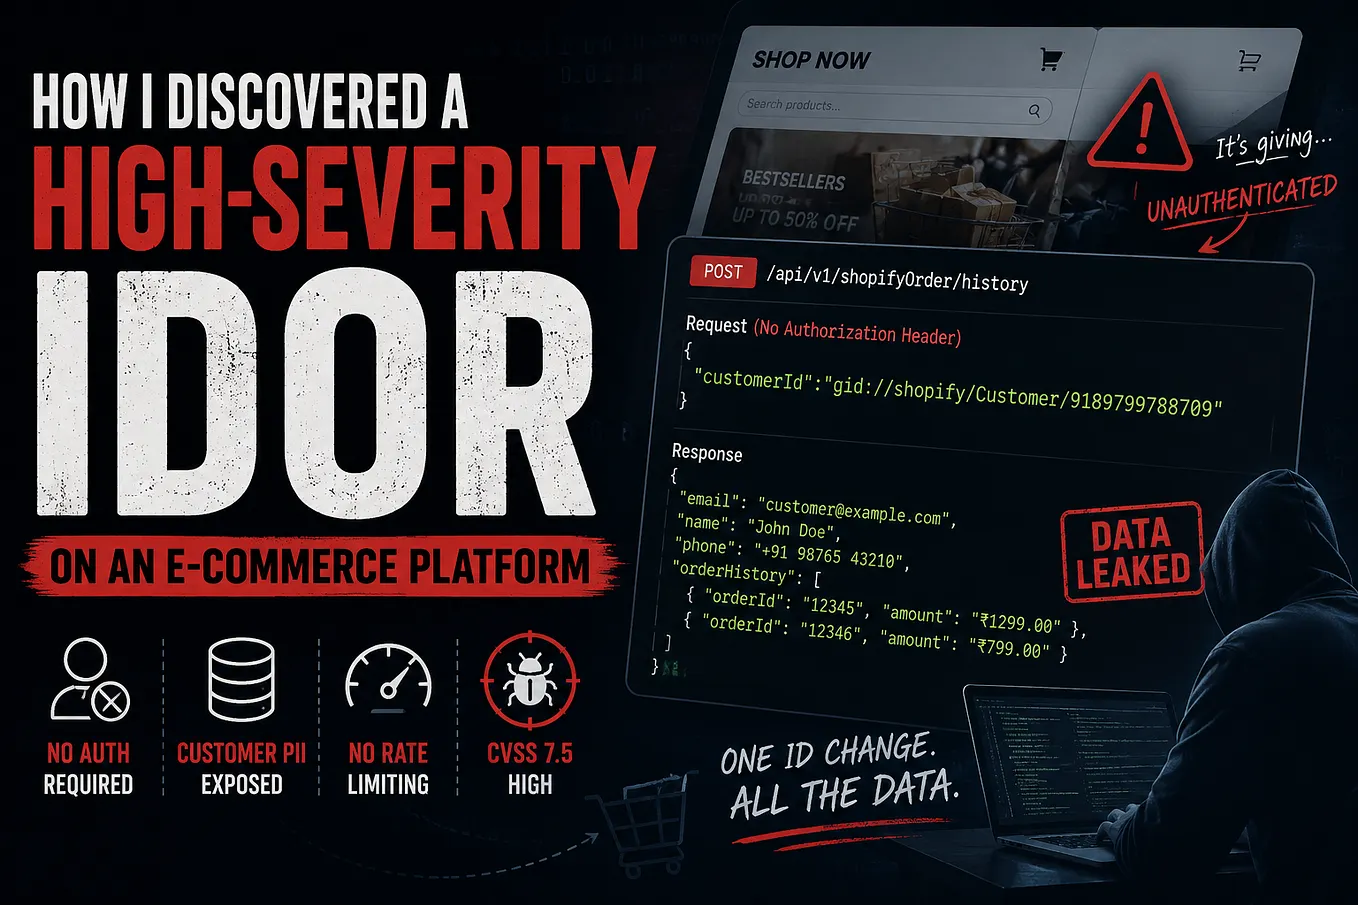
IDOR happens when a user can access or modify resources that belong to other users
by simply changing an identifier such as user_id, order_id, or file_id.
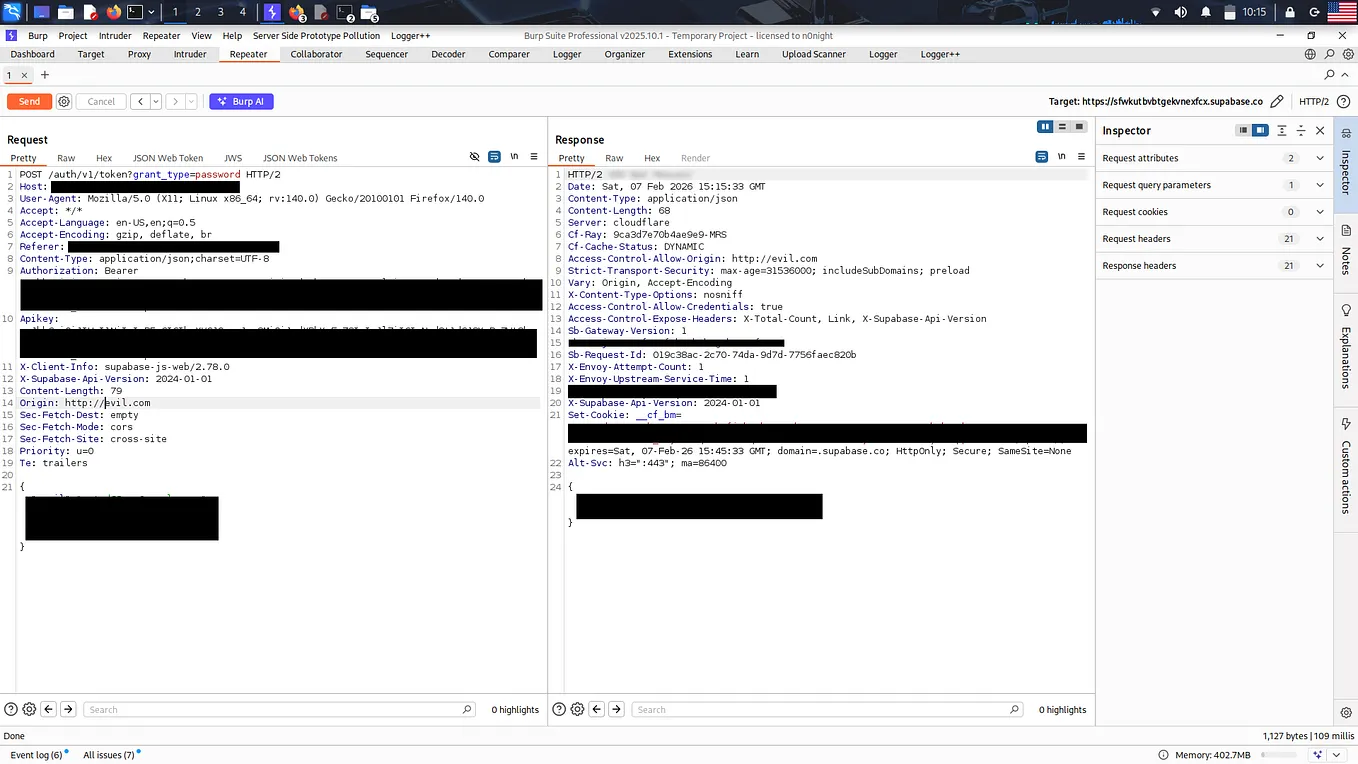
During reconnaissance, I noticed an API endpoint that retrieves user profile data
based on a numeric ID parameter.
GET /rest/v1/profiles?&user_id=eq.16e4bb6d-b6c1–40ee-81e1–4030a601df83
Get Youssefelbakrey’s stories in your inbox
Join Medium for free to get updates from this writer.
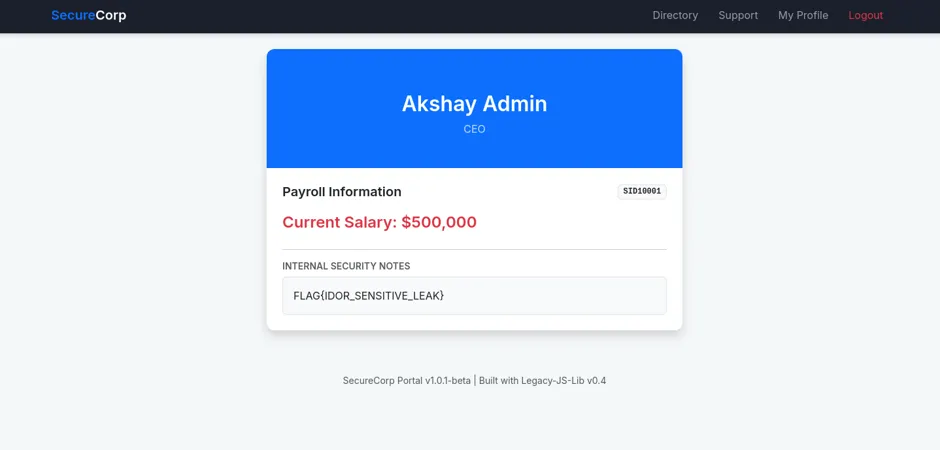
By modifying the ID parameter, I was able to access another user’s data without proper authorization.
Impact:
- Unauthorized access to sensitive user data
- Potential account takeover
- Violation of user privacy
Recommended Fix:
- Implement server-side authorization checks
- Validate object ownership before processing requests
- Avoid using predictable identifiers
IDOR vulnerabilities are easy to exploit but can have severe consequences.
Proper access control is critical for securing modern web applications.
## Tools Used
- Burp Suite
- Browser DevTools